Offline, Local-First
TOTP secrets live in your local encrypted vault; there is no cloud sync.
desktop‑2fa is an offline TOTP authenticator for people who want their second factor to live in a local encrypted vault. There is no cloud sync or account-based service.
It is CLI-first and includes an early Textual terminal UI prototype. The project uses password-based vault encryption, configurable vault paths, and commands for managing TOTP entries.
It does not replace hardware tokens or protect a compromised device. Review the security model to understand its limits.
From the 0.10.0 release tests
Real command output with synthetic accounts and credentials. Terminal frames are rendered from captured output; Textual is captured using its headless driver.
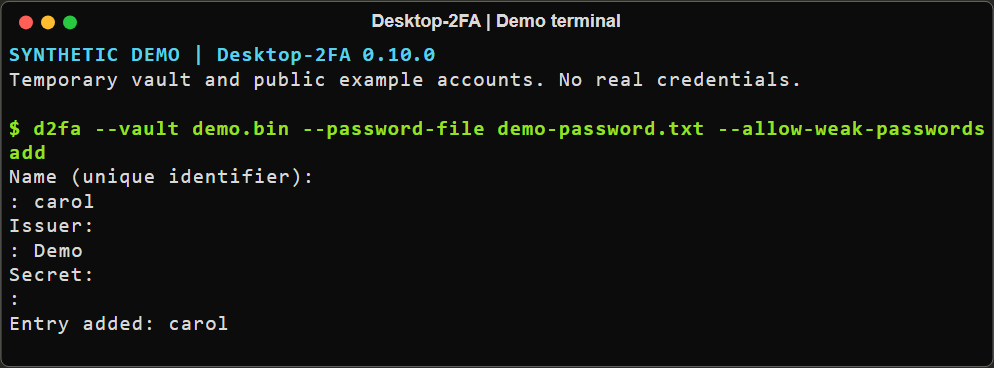
The dedicated Secret prompt hides your input. Account name and issuer remain visible.
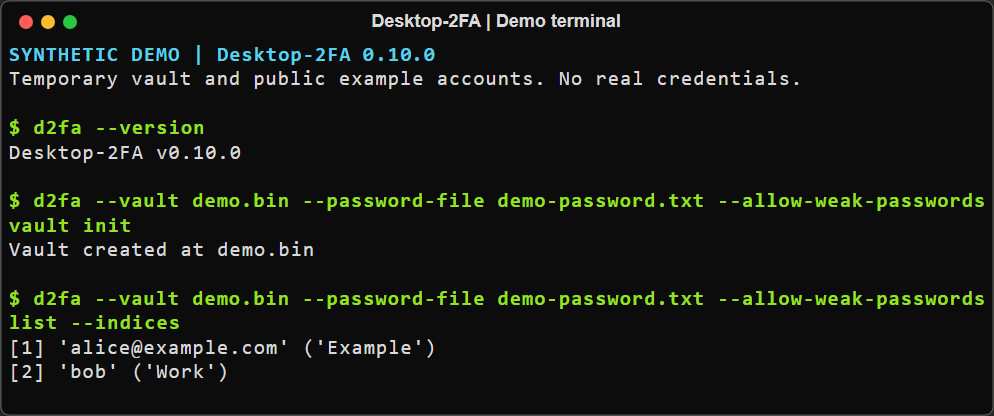
Create a vault and list accounts with one-based indices for duplicate recovery.
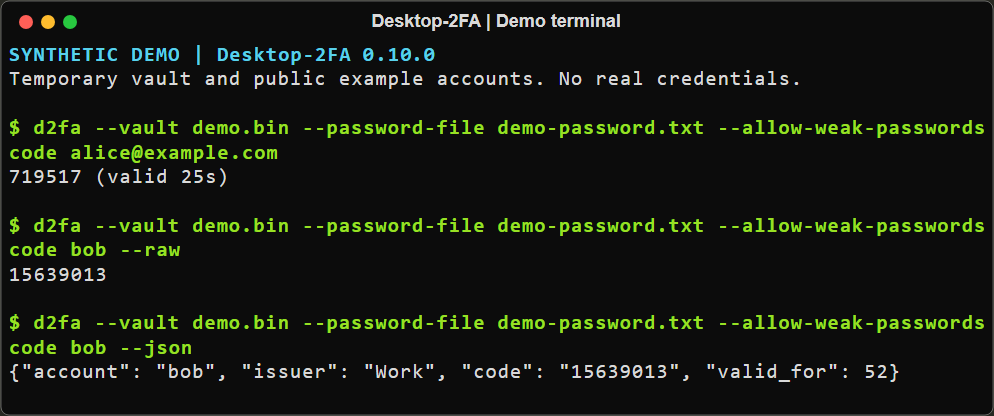
Human-readable, raw and JSON output from the same offline authenticator.
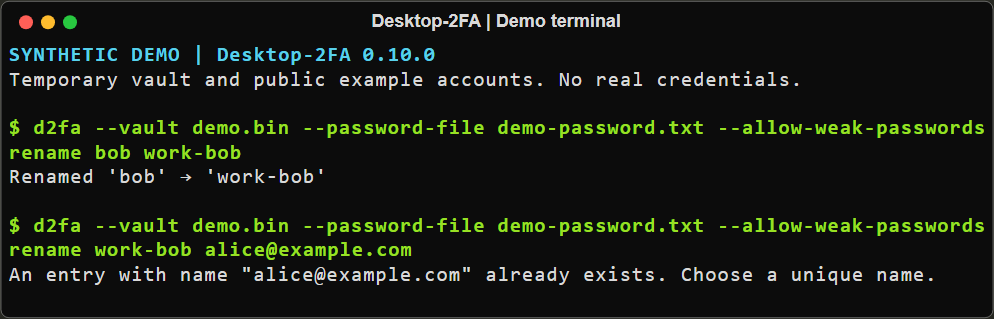
Rename entries with explicit collision refusal to preserve existing accounts.
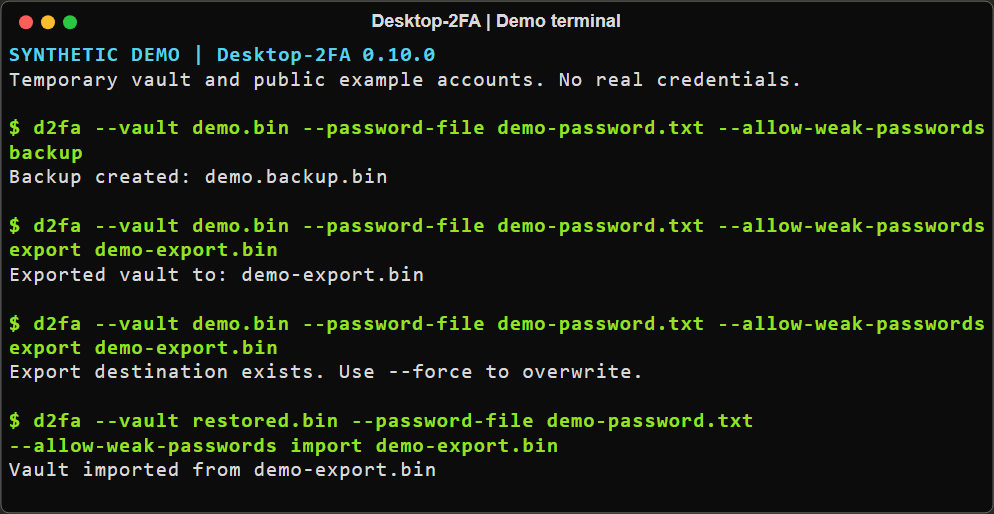
Export refuses an existing destination; recovery imports into a separate vault.
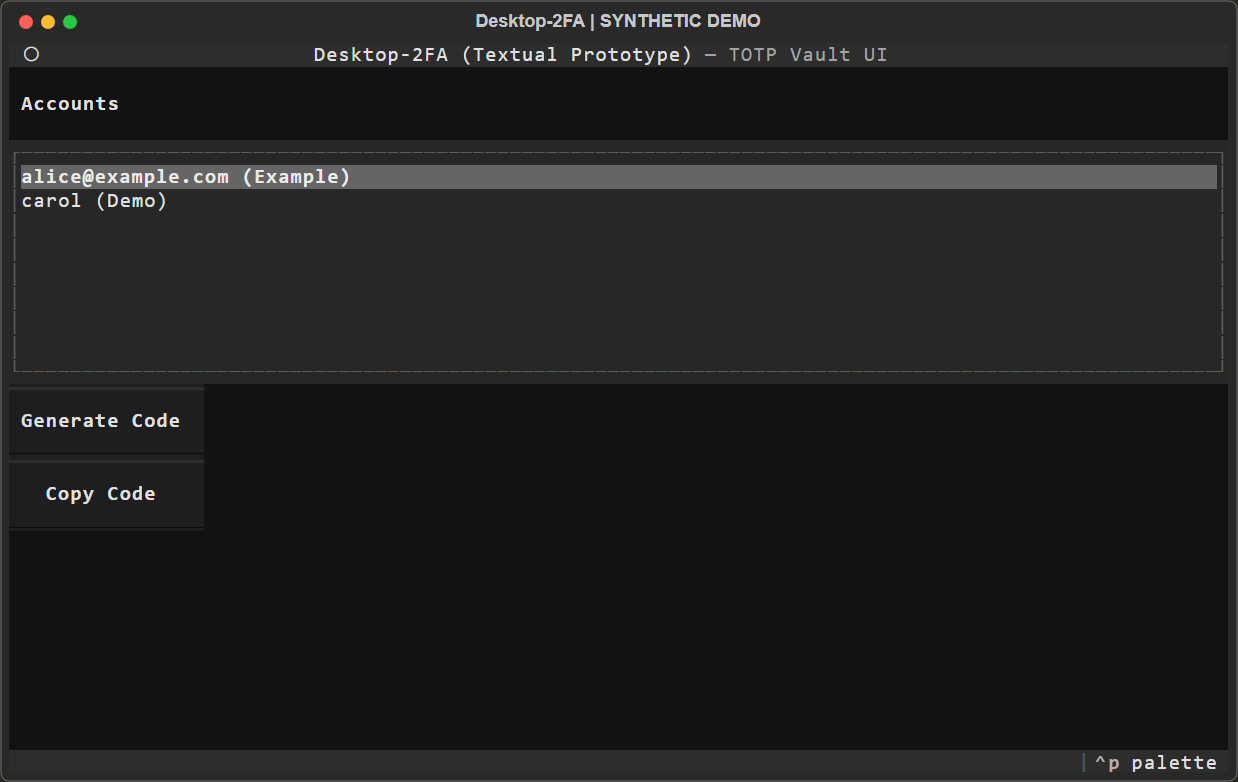
The Textual prototype lists accounts and generates or copies codes. Manage entries with the CLI.
Select an image to view it full size. Clipboard checks used a stub; these captures do not demonstrate the system clipboard or native UI behavior on every OS.
Capture method and limitations · Test campaign report (JSON)
Next on the wrist · Wear OS
An offline authenticator for Wear OS. The current MVP lets you create a vault, add accounts manually and generate TOTP codes directly on your watch.
We're working towards managing accounts on your computer and securely transferring selected ones to the watch, without cloud sync. That transfer workflow is still being designed.
Desktop-2FA remains free and open source. The Watch app is planned as a separate paid app.
The Watch app is in development; there is no download available here yet.
Requires Python 3.11 or newer. Install from PyPI:
python -m pip install desktop-2faOr install the command-line app with pipx:
pipx install desktop-2faBasic usage (interactive add hides input at the dedicated Secret prompt):
# Create a vault and add a TOTP entry
d2fa vault init
d2fa add

# Generate a code
d2fa code GitHub

# List all entries
d2fa listTOTP secrets live in your local encrypted vault; there is no cloud sync.
AES-256-GCM authenticated encryption with Argon2id password-based key derivation.
Generate RFC 6238 codes; URI-based add preserves the algorithm, digit count and time period.
A full command-line interface plus an early Textual UI prototype for viewing and copying codes.
Copy generated codes with the CLI's --copy or --copy-only options.
Choose a vault with --vault or DESKTOP_2FA_VAULT; zxcvbn evaluates password strength.
Use the default local vault or select another path with --vault or DESKTOP_2FA_VAULT.
Use d2fa add and enter a plain issuer name followed by the hidden secret. Provisioning URIs are also supported, preserving algorithm, digits and period.
Run d2fa code <name>; use --copy or --copy-only to copy the code.
Create an encrypted backup with d2fa backup and store it somewhere safe. Backups are not automatic.
Desktop-2FA does not protect secrets on a compromised device or while they are in use. See the security model and threat limits.
# Add an entry using the hidden Secret prompt
d2fa add

# Generate a code
d2fa code GitHub --copy

# List entries with indices
d2fa list --indices

# Output for scripts
d2fa code GitHub --json
d2fa code GitHub --raw

# Create an encrypted backup
d2fa backup
See the CLI reference for vault options and other commands.
| Choice | What it means |
|---|---|
| Local vault, no cloud sync | You manage backups and transfers; there is no account-based synchronization. |
| CLI-first | The complete feature set is exposed through command-line commands; the Textual UI is an early prototype. |
| Python package | Install with pip or pipx; Python 3.11 or newer is required. |
| Password recovery | There is no password reset. Users are responsible for keeping a recoverable, securely stored backup. |
This describes desktop-2fa's documented design and trade-offs, not a ranking against other authenticators.
d2fa ui). The prototype can list entries, generate codes, and copy codes, but does not manage entries or create a missing vault.otpauth:// URLs with d2fa add. QR scanning is not listed as a current feature.~/.desktop-2fa/vault. Choose another file with --vault or set DESKTOP_2FA_VAULT.Desktop-2FA 0.10.0 was released on October 30, 2026. It remains free and open source under Apache 2.0. The CLI is the primary interface; Textual is an early terminal UI prototype.
See the full changelog and source repository. Work has also started on D2FA Watch for Wear OS.